
Today
Inventories nobody can map to an agent.
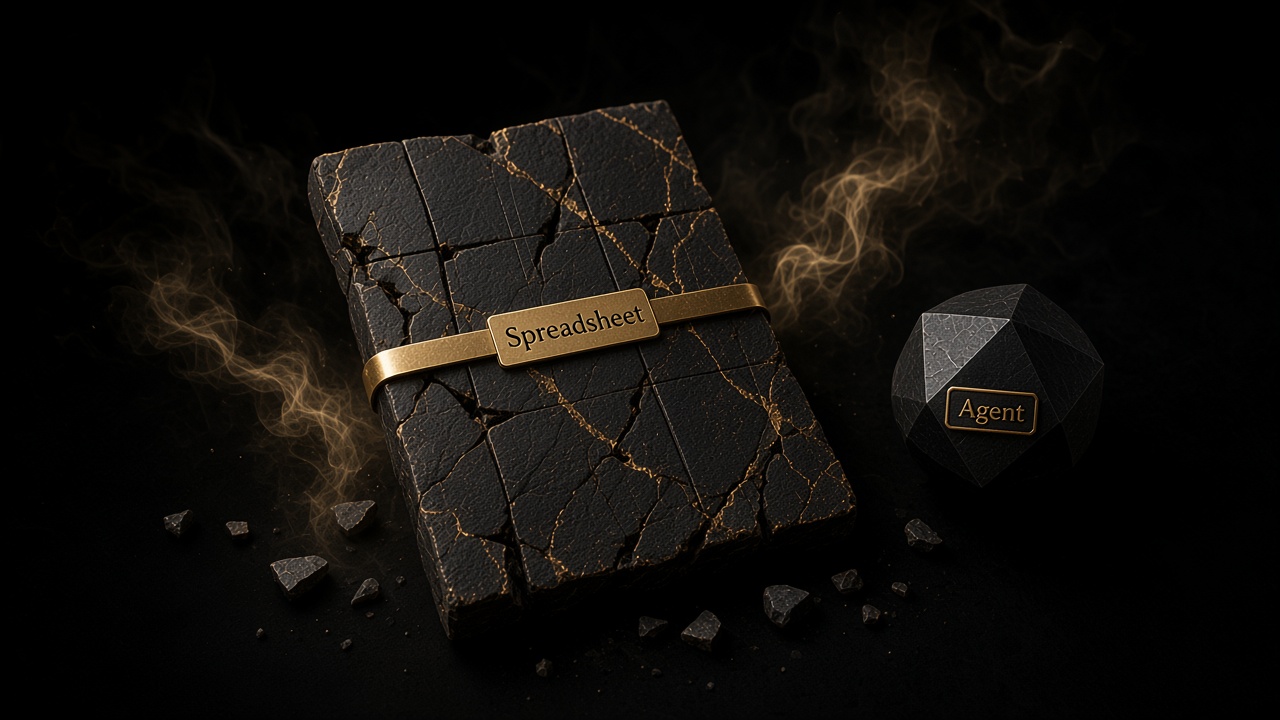
Data inventories live in spreadsheets. Nobody can say which agent, MCP server, or model can still read PII, PHI, or secrets.
- Spreadsheet
- Unknown access
- Static
- Agent
Data Security Posture Management
See which data agents can actually reach.
Zenjin Data Security Posture Management (DSPM) discovers and classifies sensitive data across the enterprise, maps how humans and AI agents can reach it, and turns that access graph into compliance evidence, not a static data catalog.
01 Scan · Stores
Six stores in the graph. Slack just connected.
PII
Classes you can prove
PHI
Mapped to identities
PCI
Stores, not rumors
Agents
On the access graph
Data Security Posture Management here is not a static catalog. Classification, identities, and attack paths sit in one posture view that updates when a source or an agent changes.
Inventory and sensitive-data views with PII, PHI, PCI, and credentials.
Who and what can reach a dataset, including non-human identities.
Attack paths, duplicates, and agent change control, not a PDF of open buckets.
Regulation mapping that feeds the same evidence trail as red teaming and evals.
A spreadsheet is not posture.
Today
Data inventories live in spreadsheets. Nobody can say which agent, MCP server, or model can still read PII, PHI, or secrets.
With Zenjin
Classification, identities, attack paths, and regulation mapping sit in one posture view that updates as sources and agents change.
From the store, through the agent, to evidence.
01
Bring in cloud stores, SaaS, and the systems your agents already touch.
02
Label sensitive data and see which identities, human and agent, can reach it.
03
Attack paths, duplicates, and agent change control show how exposure actually happens.
04
Posture maps into GDPR, HIPAA, SOC 2, PCI DSS, and the AI frameworks you already run.
Classic data security posture management tells you where sensitive data lives. Zenjin also maps how models, agents, and MCP servers can reach that data, then files the result as evidence.
We classify the data, attach identities (including agents), surface attack paths, and push findings into compliance mapping so access reviews are not a separate project.
It is posture, not a generic catalog. The point is exposure, identities, and evidence. Classification is the input, not the product.
Sensitive classes include PII, PHI, PCI, and credentials, plus the stores and identities that can reach them.
Posture and attack-path findings map into the same compliance workspace as red teaming and evals, so a data finding is already an evidence object.
Yes. When an agent or MCP path to a store changes, that is a risk finding, not a footnote in a quarterly inventory.