
Today
Agents hiding behind a human key.
Agents inherit a human’s API key or a shared service account. When a sub-agent appears, nobody can say who authorized it.
- API key
- Shared account
- Sub-agent
- Unauthorized
Agentic Identity
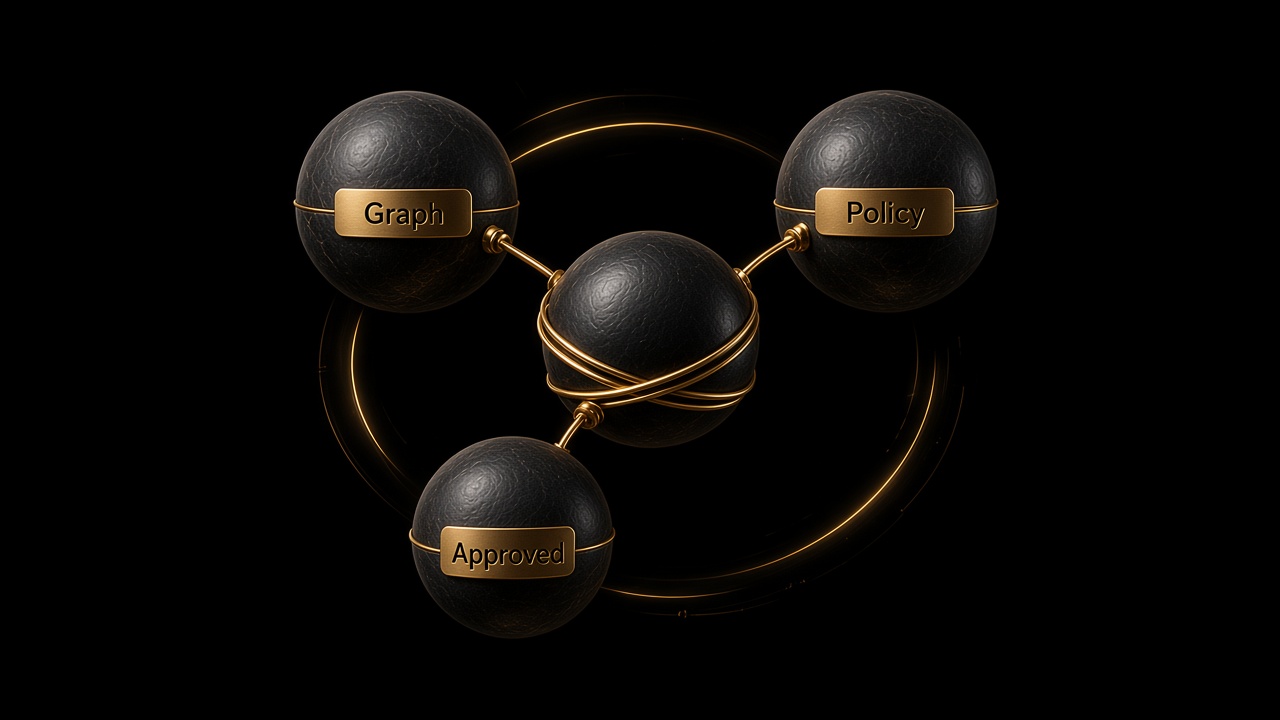
Every agent has an identity, a graph, and a policy.
Zenjin Agentic Identity gives every agent an identity, a trust graph, and policy, so you can answer who spawned it, what it can do, and who approved it.
Registry
Named, owned agents
Graph
Spawn and authority
Policy
What it may call
Approvals
When it should wait
Agents inherit a human key until someone asks. Agentic Identity binds a registry, a trust graph, policy, live violations, and an approval path.
Every agent is named, owned, and tied to an identity provider.
Spawn relationships and authority, not a flat list of bots.
What an agent may call, spawn, or spend.
Violations surface in the moment; approvals are part of the product.
A shared key is not an identity.
Today
Agents inherit a human’s API key or a shared service account. When a sub-agent appears, nobody can say who authorized it.
With Zenjin
Tenant IdP defaults, a registry, a trust graph, policy rules, live runs, violations, and an approval path.
Bind the agent, draw the spawn graph, approve what should not auto-allow.
01
Tenant IdP defaults and an agent registry. Agents are identities, not strings in a config.
02
See spawn chains, tools, and who sits above whom.
03
Policy rules, live-run violations, and human approval when the system should not auto-allow.
SSO is the floor. The product is registry, trust graph, policy, live violations, and approvals: identity that answers who authorized that.
The graph records the spawn. Policy decides if it is allowed. If not, it becomes a violation or an approval, not a surprise in production.
A run is checked against identity and policy as it happens. Unused tools stay on the graph as unused. Approvals fire when the system should not auto-allow.
Tenant IdP defaults bind agents to the directory you already run. Agents are identities, not strings in a config.
Spawn relationships, tools, and authority: who sits above whom, and which keys or tools a run actually used.
Policy decides. Some violations are recorded for review. Some require human approval before the next call.