
Today
Fragmented and unknown.
Evidence is screenshots in tickets. Mapping a finding to EU AI Act or ISO 42001 takes a week and is stale the next day.
- Siloed
- Incomplete
- Hard to trace
- Manual
Compliance
Technical findings become audit packets.
Zenjin Compliance maps technical findings from Data Security Posture Management, agentic red teaming, and AI evaluation to the frameworks you run, including EU AI Act, ISO 42001, NIST AI RMF, GDPR, HIPAA, SOC 2, and more, and keeps audit evidence current as systems change.
EU AI Act
In the catalog
ISO 42001
Mapped to findings
NIST AI RMF
Same packet
SOC 2
Fed by live product
Data Security Posture Management, red teaming, and evals write into controls. Observability and identity can attach runtime and approval evidence. The packet stays current because it is the same system.
Live posture instead of a quarterly PowerPoint.
Regulations management and a controls library you can extend.
Control mapping and regulation-to-application relationships.
Packets that stay current because the products producing findings are the same system.
Same data. A completely different outcome.
Today
Evidence is screenshots in tickets. Mapping a finding to EU AI Act or ISO 42001 takes a week and is stale the next day.
With Zenjin
Workspace, controls library, regulation mapping, attestation, and packets fed by live product findings.
From discovery to a defensible record.
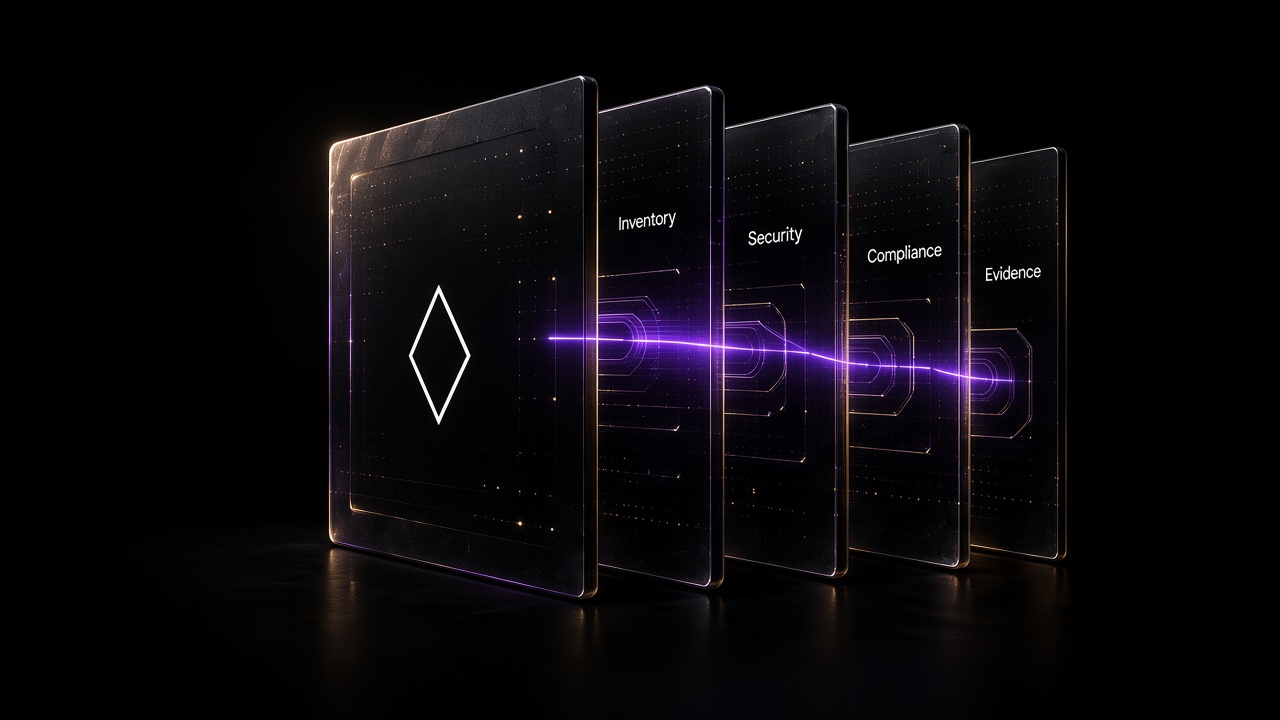
01
AI and data regulations you actually operate, including custom internal ones.
02
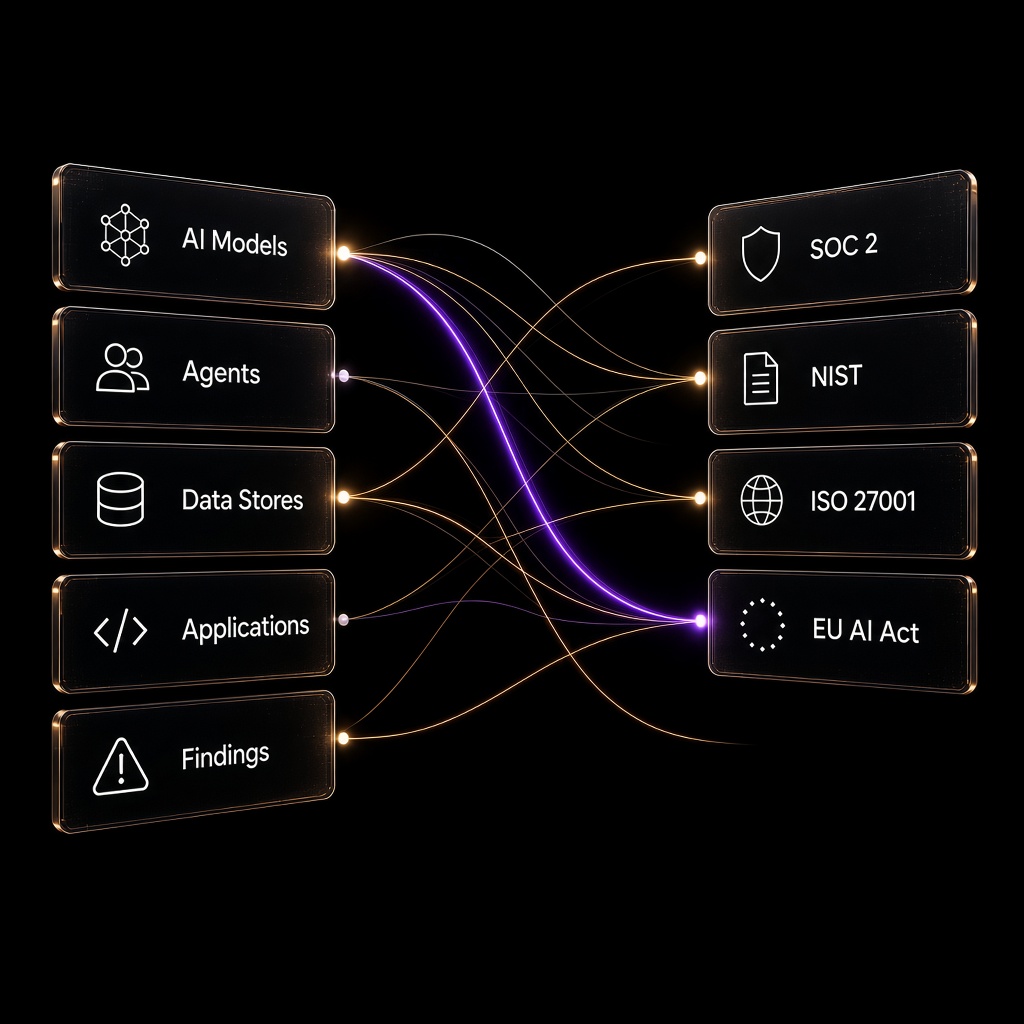
Findings from Data Security Posture Management, agentic red teaming, and evals attach to controls, not a sidebar spreadsheet.
03
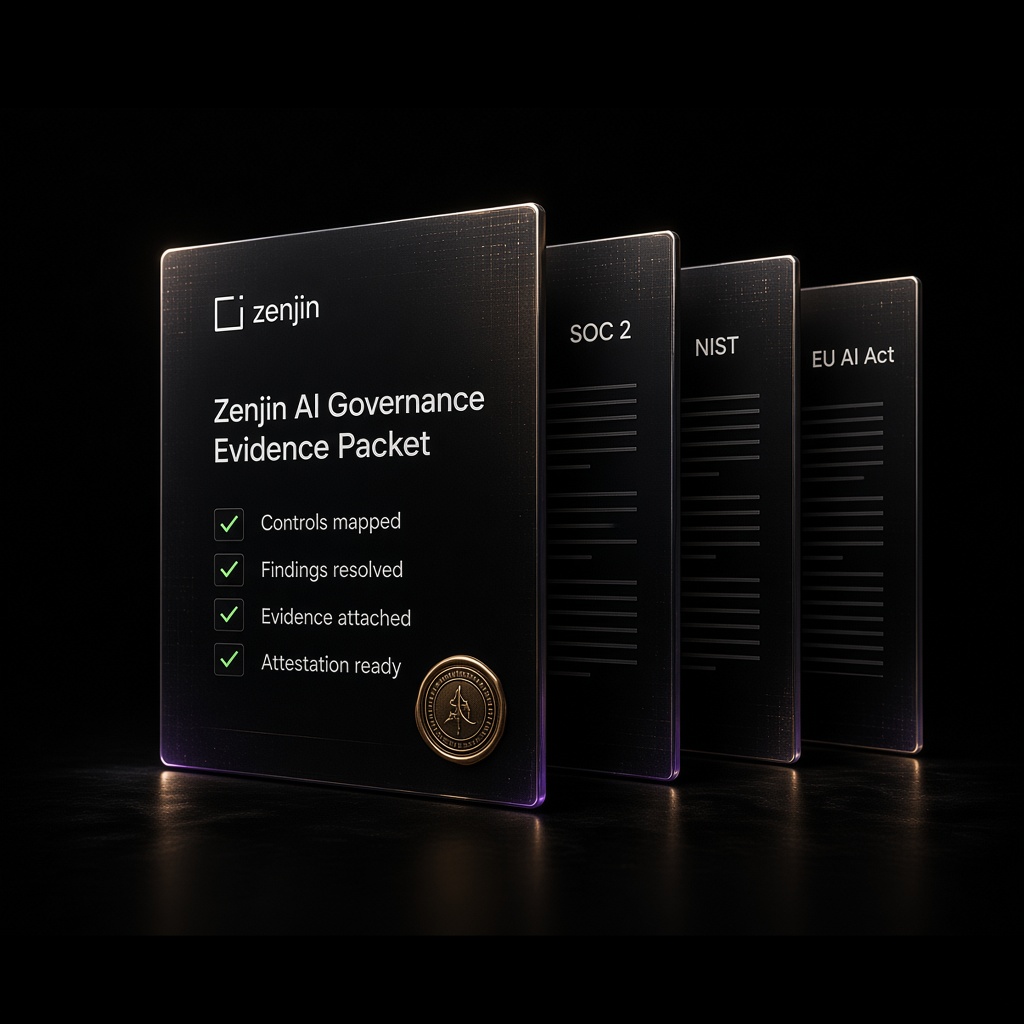
Workspace posture, attestation, and an audit-ready packet.
AI and model: EU AI Act, ISO/IEC 42001, NIST AI RMF, SR 11-7, DORA, and others in the catalog. Data and security: GDPR, HIPAA, SOC 2, PCI DSS, CCPA/CPRA, ISO 27001, NIST CSF. Custom internal frameworks are supported. We confirm the live catalog per tenant.
No. Policy-only GRC writes documents. Zenjin Compliance is the evidence plane for technical findings from the rest of the platform.
Data Security Posture Management, agentic red teaming, and AI evaluation write into controls. Observability and identity can attach runtime and approval evidence to the same packet.
Yes. Custom internal frameworks sit next to the catalog ones, with the same mapping and attestation path.
It stays current because the products producing findings are the same system. You are not pasting screenshots into a ticket a week later.
Yes. Workspace posture, control mapping, and attestation export as an audit-ready packet.